USA // WEST COAST
Enterprise AI Global West Coast
500+ AI, data and technology leaders at the Hyatt Regency San Francisco comparing what actually works in production.
500+ AI, data and technology leaders at the Hyatt Regency San Francisco comparing what actually works in production.
Enterprise AI has moved past the question of whether it works. The question now is which platforms it runs on, what it costs at scale, and who is accountable when it acts.
Enterprise AI Global puts the engineers building AI systems and the leaders deciding where AI goes next in the same room. Two streams run under one roof: AI Engineering and Infrastructure, and Enterprise AI Strategy and Transformation.
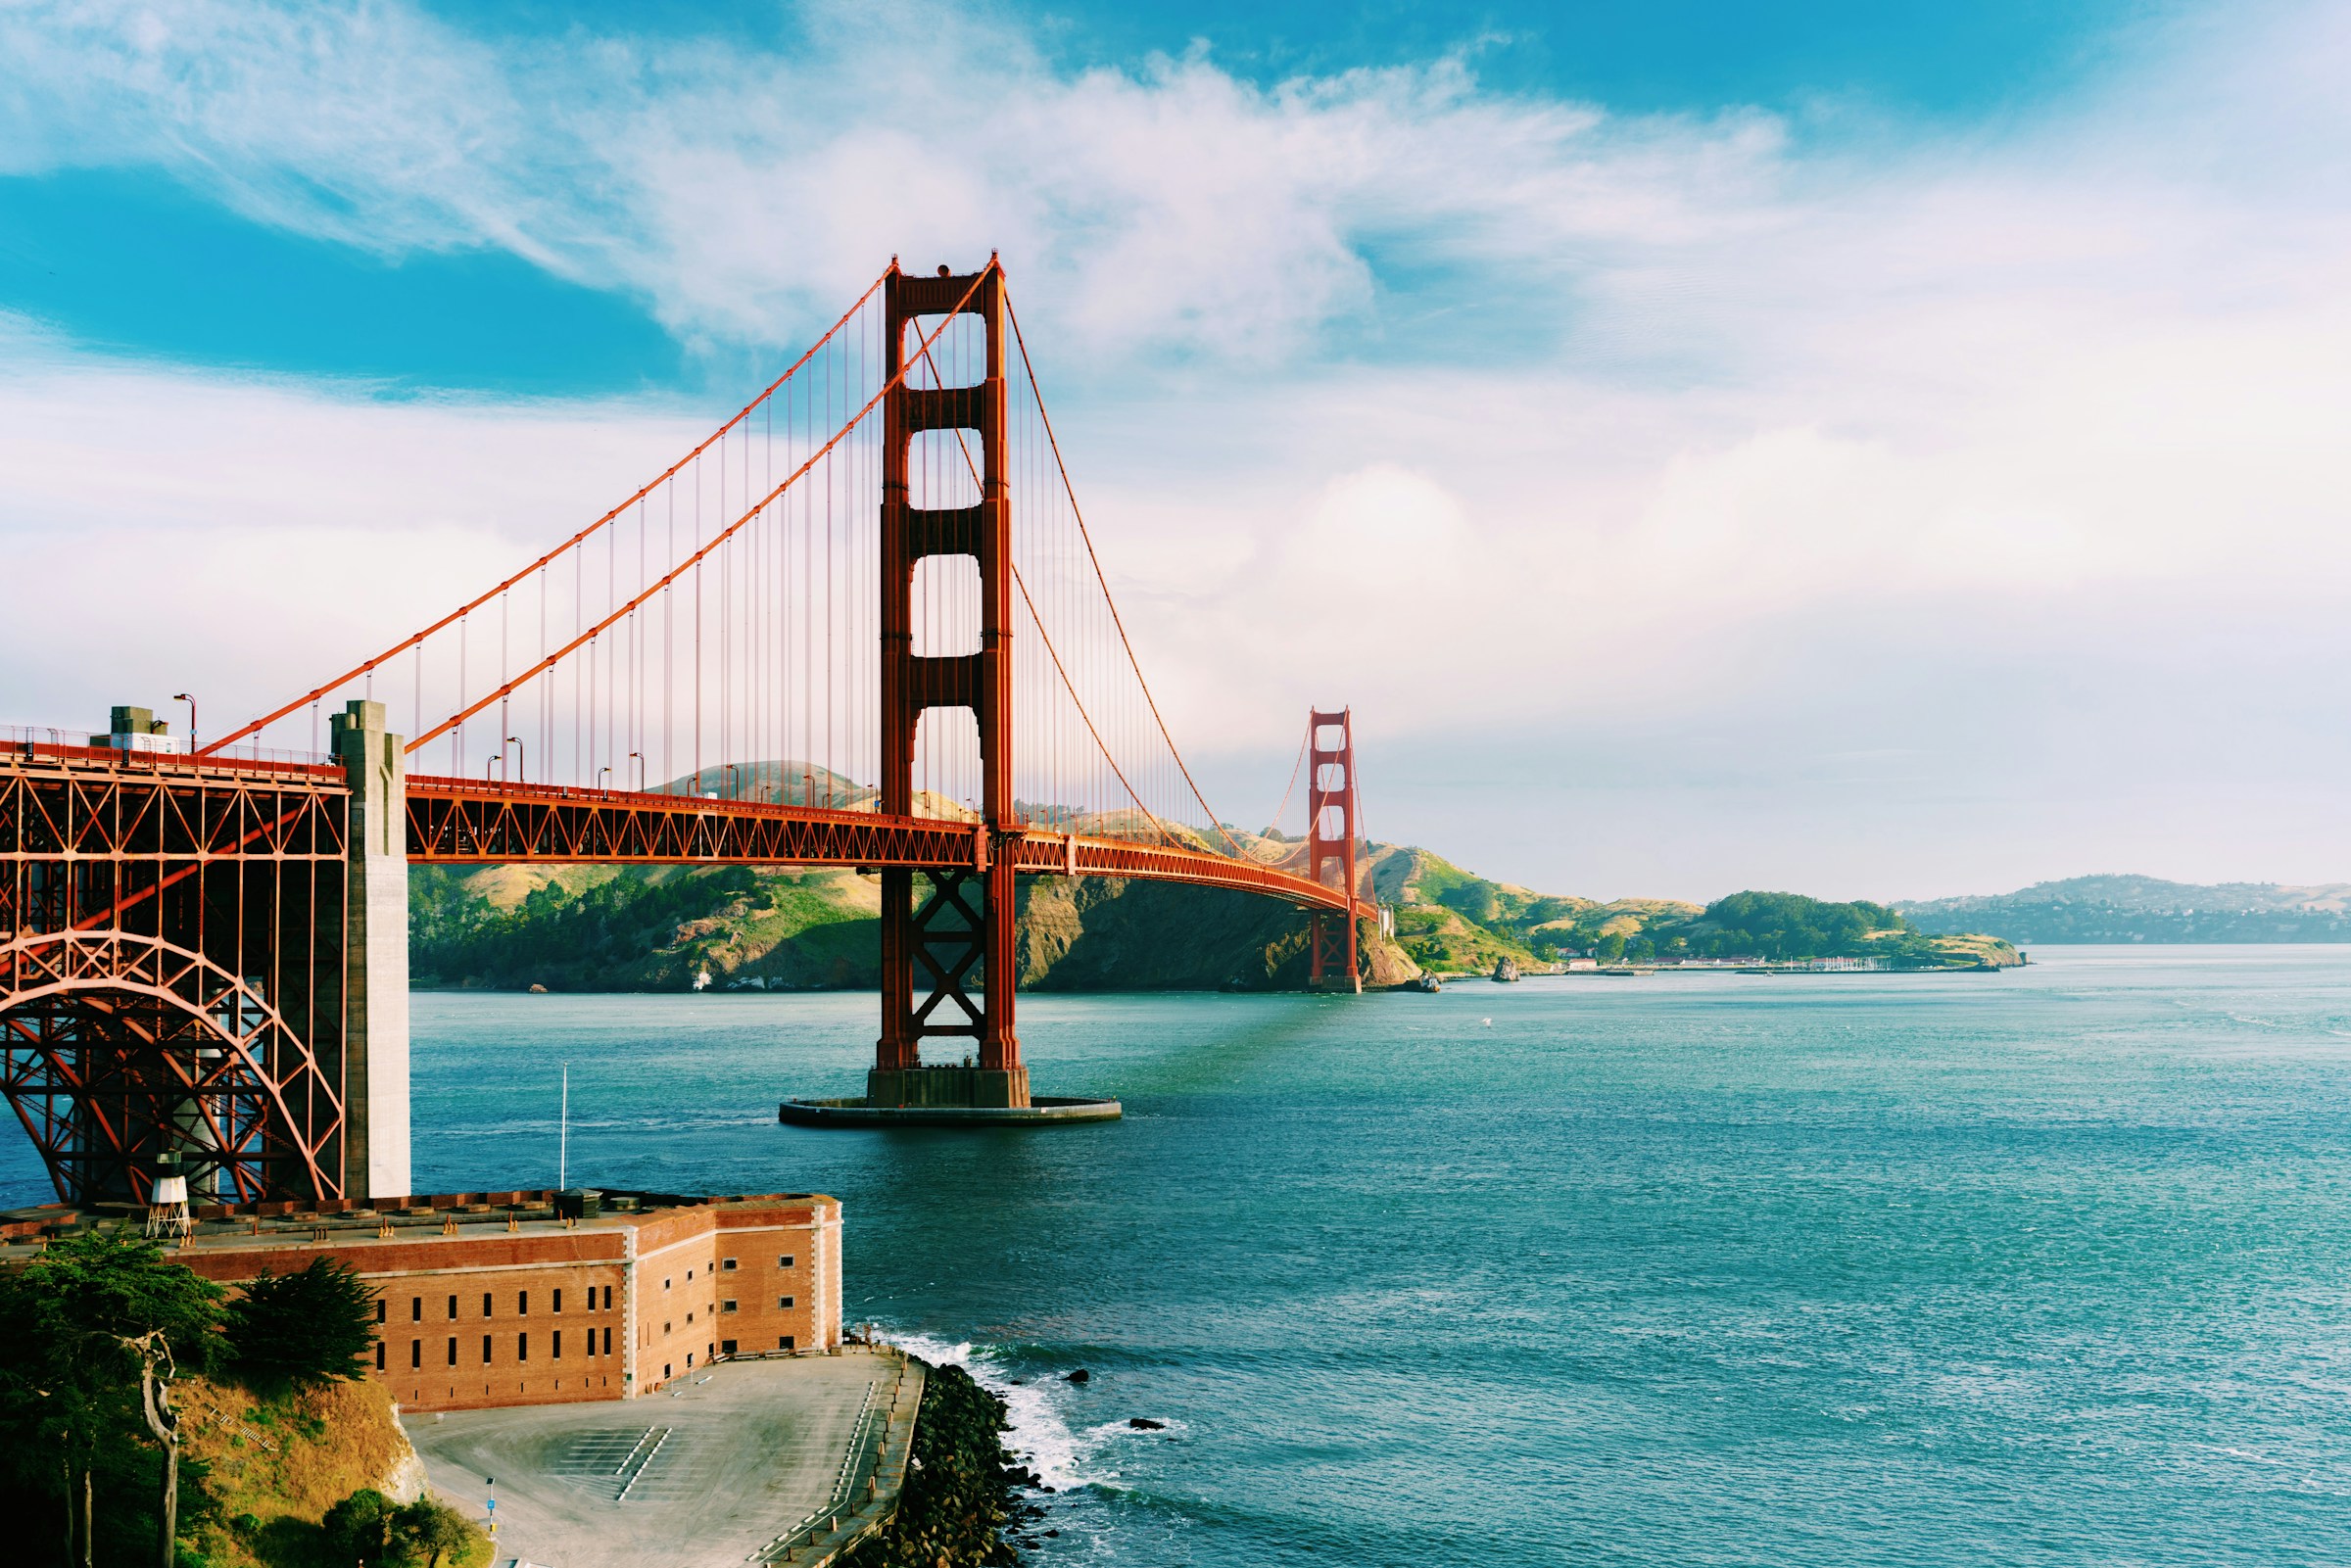
The West Coast edition runs at the Hyatt Regency San Francisco on October 21, with 500+ AI, data and technology leaders from 300+ organizations across North America, and 24 partner organizations in the room.
Every attendee is a practitioner. No vendors in the audience, so the conversations are candid and the comparisons are real.
Roundtables, think tanks and audience activities, with two of the day's hours given over to breaks and networking by design.
The CISOs, Heads of IAM and identity architects running workforce identity, CIAM, IGA and PAM at large enterprises.
PLACEHOLDER — workforce identity, CIAM, IGA and PAM landing on the same team, and how the best programmes are structured.
PLACEHOLDER — non-human identities and AI agents as first-class principals, and what governance actually looks like.
PLACEHOLDER — access governance under regulator pressure, and how to evidence maturity without stalling delivery.
Ten partners maximum per event. That cap is what keeps booth engagement and meeting quality high.
PLACEHOLDER — workforce identity, customer identity, privileged access, machine identities and now AI agents all land on the same teams, while credential-based attacks remain a leading cause of breaches.
PLACEHOLDER — at most security conferences IAM is a stream inside a much broader event. Here it is the whole room, which changes what people are willing to say.
PLACEHOLDER — content is guided by a community of 500+ professionals, so the agenda reflects what teams are actually shipping rather than what vendors want to present.
Short, sharp and interactive. Two hours of the day are breaks and networking by design.
Beat the rush and join us early for complimentary barista-made coffee and breakfast.
Beat the rush and join us early for complimentary barista-made coffee and breakfast.
Beat the rush and join us early for complimentary barista-made coffee and breakfast.
Beat the rush and join us early for complimentary barista-made coffee and breakfast.
Beat the rush and join us early for complimentary barista-made coffee and breakfast.
Kick off the day with a welcome from your MC and a look at what's ahead.
Kick off the day with a welcome from your MC and a look at what's ahead.
Kick off the day with a welcome from your MC and a look at what's ahead.
Kick off the day with a welcome from your MC and a look at what's ahead.
Kick off the day with a welcome from your MC and a look at what's ahead.
Identity has become one of the biggest security risks facing organisations. As machine identities grow rapidly and AI agents begin acting on behalf of people, traditional approaches to identity and access are no longer enough.
This keynote explores why identity is now central to enterprise security, what's driving this change, and how organisations can prepare for 2027.
Identity has become one of the biggest security risks facing organizations. As machine identities grow rapidly and AI agents begin acting on behalf of people, traditional approaches to identity and access are no longer enough.
This keynote explores why identity is now central to enterprise security, what's driving this change, and how organizations can prepare for 2027.
With Australia's Digital ID system now opening to the private sector under the Digital ID Act, organisations face a genuine strategic choice: become an accredited relying party, wait, or build alongside. This keynote unpacks where the rollout actually stands, the accreditation and cost realities of myID and the AGDIS, and how leading organisations are turning verified digital identity from a compliance obligation into a trust and onboarding advantage.
Okta and Deloitte present a blueprint for unifying identity governance across employees, contractors and machine workloads in hybrid and multi-cloud environments — and what it takes to run one security fabric across all of them.
Government-backed and industry digital identity schemes are moving into mainstream private-sector use. This keynote unpacks where adoption really stands, the practical requirements of taking part, and how verified digital identity reshapes onboarding and fraud reduction — and the trade-offs on the way.
Government-backed and industry digital identity schemes are moving into mainstream private-sector use. This keynote unpacks where adoption really stands, the practical requirements of taking part, and how verified digital identity reshapes onboarding and fraud reduction — and the trade-offs on the way.
Government-backed and industry digital identity schemes are moving into mainstream private-sector use. This keynote unpacks where adoption really stands, the practical requirements of taking part, and how verified digital identity reshapes onboarding and fraud reduction — and the trade-offs on the way.
Autonomous AI agents are now provisioning access, calling APIs, and making decisions on users' behalf, yet most organisations have no framework to govern them. This panel brings together security leaders wrestling with the non-human identity governance vacuum: how to authenticate, authorise, monitor, and revoke identities that never sleep, multiply fast, and increasingly act on their own.
Autonomous AI agents are now provisioning access, calling APIs, and making decisions on users' behalf, yet most organisations have no framework to govern them. This panel brings together security leaders wrestling with the non-human identity governance vacuum: how to authenticate, authorise, monitor, and revoke identities that never sleep, multiply fast, and increasingly act on their own.
Autonomous AI agents are now provisioning access, calling APIs, and making decisions on users' behalf, yet most organisations have no framework to govern them. This panel brings together security leaders wrestling with the non-human identity governance vacuum: how to authenticate, authorise, monitor, and revoke identities that never sleep, multiply fast, and increasingly act on their own.
Autonomous AI agents are now provisioning access, calling APIs, and making decisions on users' behalf, yet most organizations have no framework to govern them. This panel brings together security leaders wrestling with the non-human identity governance vacuum: how to authenticate, authorize, monitor, and revoke identities that never sleep, multiply fast, and increasingly act on their own.
Autonomous AI agents are now provisioning access, calling APIs, and making decisions on users' behalf, yet most organizations have no framework to govern them. This panel brings together security leaders wrestling with the non-human identity governance vacuum: how to authenticate, authorize, monitor, and revoke identities that never sleep, multiply fast, and increasingly act on their own.
With passkeys crossing into the mainstream and a large majority of enterprises now deploying them, passwordless is no longer aspirational. In this case study, a practitioner walks through a real phishing-resistant authentication rollout — the pilot, the pushback, the edge cases (shared devices, legacy apps, deskless workers), and the measurable impact on help-desk load and account takeover.
With passkeys crossing into the mainstream and a large majority of enterprises now deploying them, passwordless is no longer aspirational. In this case study, a practitioner walks through a real phishing-resistant authentication rollout — the pilot, the pushback, the edge cases (shared devices, legacy apps, deskless workers), and the measurable impact on help-desk load and account takeover.
With passkeys crossing into the mainstream and a large majority of enterprises now deploying them, passwordless is no longer aspirational. In this case study, a practitioner walks through a real phishing-resistant authentication rollout — the pilot, the pushback, the edge cases (shared devices, legacy apps, deskless workers), and the measurable impact on help-desk load and account takeover.
With passkeys crossing into the mainstream and a large majority of enterprises now deploying them, passwordless is no longer aspirational. In this case study, a practitioner walks through a real phishing-resistant authentication rollout — the pilot, the pushback, the edge cases (shared devices, legacy apps, deskless workers), and the measurable impact on help-desk load and account takeover.
With passkeys crossing into the mainstream and a large majority of enterprises now deploying them, passwordless is no longer aspirational. In this case study, a practitioner walks through a real phishing-resistant authentication rollout — the pilot, the pushback, the edge cases (shared devices, legacy apps, deskless workers), and the measurable impact on help-desk load and account takeover.
Recharge with refreshments and structured networking with your peers.
Recharge with refreshments and structured networking with your peers.
Recharge with refreshments and structured networking with your peers.
Recharge with refreshments and structured networking with your peers.
Recharge with refreshments and structured networking with your peers.
A hands-on, interactive session working through a real identity and access scenario as a room. Details announced soon.
A hands-on, interactive session working through a real identity and access scenario as a room. Details announced soon.
A hands-on, interactive session working through a real identity and access scenario as a room. Details announced soon.
A hands-on, interactive session working through a real identity and access scenario as a room. Details announced soon.
A hands-on, interactive session working through a real identity and access scenario as a room. Details announced soon.
Standing privileges remain the fastest path from a single compromised credential to full breach. This case study details how one organisation re-architected privileged access management inside a zero-trust model and wired it into identity threat detection and response (ITDR), moving from static admin accounts to just-in-time access with live detection of identity-based attacks.
Standing privileges remain the fastest path from a single compromised credential to full breach. This case study details how one organisation re-architected privileged access management inside a zero-trust model and wired it into identity threat detection and response (ITDR), moving from static admin accounts to just-in-time access with live detection of identity-based attacks.
Standing privileges remain the fastest path from a single compromised credential to full breach. This case study details how one organisation re-architected privileged access management inside a zero-trust model and wired it into identity threat detection and response (ITDR), moving from static admin accounts to just-in-time access with live detection of identity-based attacks.
Standing privileges remain the fastest path from a single compromised credential to full breach. This case study details how one organization re-architected privileged access management inside a zero-trust model and wired it into identity threat detection and response (ITDR), moving from static admin accounts to just-in-time access with live detection of identity-based attacks.
Standing privileges remain the fastest path from a single compromised credential to full breach. This case study details how one organization re-architected privileged access management inside a zero-trust model and wired it into identity threat detection and response (ITDR), moving from static admin accounts to just-in-time access with live detection of identity-based attacks.
With deepfake-driven identity fraud surging sharply in 2026 and synthetic-voice attacks targeting help desks and executives, traditional verification is failing. In this case study, a leader shares how their organisation hardened identity proofing and high-risk transactions against generative-AI impersonation across the contact centre, executive workflows, and customer onboarding.
With deepfake-driven identity fraud surging sharply in 2026 and synthetic-voice attacks targeting help desks and executives, traditional verification is failing. In this case study, a leader shares how their organisation hardened identity proofing and high-risk transactions against generative-AI impersonation across the contact centre, executive workflows, and customer onboarding.
With deepfake-driven identity fraud surging sharply in 2026 and synthetic-voice attacks targeting help desks and executives, traditional verification is failing. In this case study, a leader shares how their organisation hardened identity proofing and high-risk transactions against generative-AI impersonation across the contact centre, executive workflows, and customer onboarding.
With deepfake-driven identity fraud surging sharply in 2026 and synthetic-voice attacks targeting help desks and executives, traditional verification is failing. In this case study, a leader shares how their organization hardened identity proofing and high-risk transactions against generative-AI impersonation across the contact center, executive workflows, and customer onboarding.
With deepfake-driven identity fraud surging sharply in 2026 and synthetic-voice attacks targeting help desks and executives, traditional verification is failing. In this case study, a leader shares how their organization hardened identity proofing and high-risk transactions against generative-AI impersonation across the contact center, executive workflows, and customer onboarding.
NIST's post-quantum standards are final and migration deadlines are now set, but identity systems — certificates, tokens, signing keys — are among the hardest things to make crypto-agile. Harvest now, decrypt later makes this urgent even before quantum computers arrive. This panel maps a realistic path from crypto-inventory to migration for the identity stack specifically.
NIST's post-quantum standards are final and migration deadlines are now set, but identity systems — certificates, tokens, signing keys — are among the hardest things to make crypto-agile. Harvest now, decrypt later makes this urgent even before quantum computers arrive. This panel maps a realistic path from crypto-inventory to migration for the identity stack specifically.
Post-quantum standards are final and migration deadlines are now set, but identity systems — certificates, tokens, signing keys — are among the hardest things to make crypto-agile. Harvest now, decrypt later makes this urgent even before quantum computers arrive. This panel maps a realistic path from crypto-inventory to migration for the identity stack specifically.
NIST's post-quantum standards are final and migration deadlines are now set, but identity systems — certificates, tokens, signing keys — are among the hardest things to make crypto-agile. Harvest now, decrypt later makes this urgent even before quantum computers arrive. This panel maps a realistic path from crypto-inventory to migration for the identity stack specifically.
NIST's post-quantum standards are final and migration deadlines are now set, but identity systems — certificates, tokens, signing keys — are among the hardest things to make crypto-agile. Harvest now, decrypt later makes this urgent even before quantum computers arrive. This panel maps a realistic path from crypto-inventory to migration for the identity stack specifically.
Small-group, discussion-based sessions where you'll work through real identity and access challenges with peers in similar roles. Roundtable topics will be announced soon.
Small-group, discussion-based sessions where you'll work through real identity and access challenges with peers in similar roles. Roundtable topics will be announced soon.
Small-group, discussion-based sessions where you'll work through real identity and access challenges with peers in similar roles. Roundtable topics will be announced soon.
Small-group, discussion-based sessions where you'll work through real identity and access challenges with peers in similar roles. Roundtable topics will be announced soon.
Small-group, discussion-based sessions where you'll work through real identity and access challenges with peers in similar roles. Roundtable topics will be announced soon.
Enjoy a complimentary lunch while connecting with fellow attendees.
Enjoy a complimentary lunch while connecting with fellow attendees.
Enjoy a complimentary lunch while connecting with fellow attendees.
Enjoy a complimentary lunch while connecting with fellow attendees.
Enjoy a complimentary lunch while connecting with fellow attendees.
Put your knowledge to the test in this fast-paced quiz covering real-world trivia, key concepts, and emerging trends. Compete for bragging rights — and a travel voucher — as the top scorer takes the crown.
Put your knowledge to the test in this fast-paced quiz covering real-world trivia, key concepts, and emerging trends. Compete for bragging rights — and a travel voucher — as the top scorer takes the crown.
Put your knowledge to the test in this fast-paced quiz covering real-world trivia, key concepts, and emerging trends. Compete for bragging rights — and a voucher — as the top scorer takes the crown.
Put your knowledge to the test in this fast-paced quiz covering real-world trivia, key concepts, and emerging trends. Compete for bragging rights — and a travel voucher — as the top scorer takes the crown.
Put your knowledge to the test in this fast-paced quiz covering real-world trivia, key concepts, and emerging trends. Compete for bragging rights — and a travel voucher — as the top scorer takes the crown.
Most organisations don't have one IAM problem — they have a decade of them stitched together: legacy directories, M&A leftovers, siloed cloud IAM, and a team too stretched to fix it properly. This case study follows a practitioner who consolidated a genuinely fragmented identity estate without a green-field budget or headcount, showing what got prioritised, what got cut, and how they built internal buy-in to sustain it.
Most organisations don't have one IAM problem — they have a decade of them stitched together: legacy directories, M&A leftovers, siloed cloud IAM, and a team too stretched to fix it properly. This case study follows a practitioner who consolidated a genuinely fragmented identity estate without a green-field budget or headcount, showing what got prioritised, what got cut, and how they built internal buy-in to sustain it.
Most organisations don't have one IAM problem — they have a decade of them stitched together: legacy directories, M&A leftovers, siloed cloud IAM, and a team too stretched to fix it properly. This case study follows a practitioner who consolidated a genuinely fragmented identity estate without a green-field budget or headcount, showing what got prioritised, what got cut, and how they built internal buy-in to sustain it.
Most organizations don't have one IAM problem — they have a decade of them stitched together: legacy directories, M&A leftovers, siloed cloud IAM, and a team too stretched to fix it properly. This case study follows a practitioner who consolidated a genuinely fragmented identity estate without a green-field budget or headcount, showing what got prioritized, what got cut, and how they built internal buy-in to sustain it.
Most organizations don't have one IAM problem — they have a decade of them stitched together: legacy directories, M&A leftovers, siloed cloud IAM, and a team too stretched to fix it properly. This case study follows a practitioner who consolidated a genuinely fragmented identity estate without a green-field budget or headcount, showing what got prioritized, what got cut, and how they built internal buy-in to sustain it.
As biometrics and behavioural signals become core to authentication, the hardest questions are no longer technical but ethical: consent, bias, proportionality, and what happens when identity data is compromised. This closing keynote argues that durable identity security is as much cultural as technical, and lays out how to embed privacy-respecting, identity-first thinking across the whole organisation.
As biometrics and behavioural signals become core to authentication, the hardest questions are no longer technical but ethical: consent, bias, proportionality, and what happens when identity data is compromised. This closing keynote argues that durable identity security is as much cultural as technical, and lays out how to embed privacy-respecting, identity-first thinking across the whole organisation.
As biometrics and behavioural signals become core to authentication, the hardest questions are no longer technical but ethical: consent, bias, proportionality, and what happens when identity data is compromised. This closing keynote argues that durable identity security is as much cultural as technical, and lays out how to embed privacy-respecting, identity-first thinking across the whole organisation.
As biometrics and behavioral signals become core to authentication, the hardest questions are no longer technical but ethical: consent, bias, proportionality, and what happens when identity data is compromised. This closing keynote argues that durable identity security is as much cultural as technical, and lays out how to embed privacy-respecting, identity-first thinking across the whole organization.
As biometrics and behavioral signals become core to authentication, the hardest questions are no longer technical but ethical: consent, bias, proportionality, and what happens when identity data is compromised. This closing keynote argues that durable identity security is as much cultural as technical, and lays out how to embed privacy-respecting, identity-first thinking across the whole organization.
Every organisation is fighting the same three constraints — integration, budget, and skills — while the threat surface keeps expanding. This interactive session puts the strategic trade-offs directly to the room, using live voting to surface where the audience really stands versus where the market says they should be, then debating the gaps.
Every organisation is fighting the same three constraints — integration, budget, and skills — while the threat surface keeps expanding. This interactive session puts the strategic trade-offs directly to the room, using live voting to surface where the audience really stands versus where the market says they should be, then debating the gaps.
Every organisation is fighting the same three constraints — integration, budget, and skills — while the threat surface keeps expanding. This interactive session puts the strategic trade-offs directly to the room, using live voting to surface where the audience really stands versus where the market says they should be, then debating the gaps.
Every organization is fighting the same three constraints — integration, budget, and skills — while the threat surface keeps expanding. This interactive session puts the strategic trade-offs directly to the room, using live voting to surface where the audience really stands versus where the market says they should be, then debating the gaps.
Every organization is fighting the same three constraints — integration, budget, and skills — while the threat surface keeps expanding. This interactive session puts the strategic trade-offs directly to the room, using live voting to surface where the audience really stands versus where the market says they should be, then debating the gaps.
Wrap-up of the day's key takeaways — and your chance to win some epic prizes.
Wrap-up of the day's key takeaways — and your chance to win some epic prizes.
Wrap-up of the day's key takeaways — and your chance to win some epic prizes.
Wrap-up of the day's key takeaways — and your chance to win some epic prizes.
Wrap-up of the day's key takeaways — and your chance to win some epic prizes.
Unwind with your peers for a couple of drinks on us!
Unwind with your peers for a couple of drinks on us!
Unwind with your peers for a couple of drinks on us!
Unwind with your peers for a couple of drinks on us!
Unwind with your peers for a couple of drinks on us!
See you at Identity World Melbourne on 3 March 2027.
See you at Identity World New York on May 6, 2027.
See you at Identity World San Francisco on November 3, 2027.
See you at Identity World London on June 16, 2027.
That's a wrap on the 2027 series — see you in Sydney for 2028.
Confirmed speakers for this edition. Past speakers from the series follow below.
Short, sharp and interactive by design. No slide-after-slide days.
Solo stage time from a practitioner or an invited expert, framing where the discipline is heading.
Three or four leaders comparing programmes directly, moderated to stay concrete rather than abstract.
Small-group peer discussion on a single named problem, with no audience and no slides.
How I Solved sessions: a practitioner walks through one real problem and exactly how they fixed it.
Attendees choose who they want to meet, so every meeting is relevant on both sides. Nobody is assigned a stranger.
Sponsors are not charged for a fixed number of meetings. If demand is there we keep booking them — some partners get 10 to 15 at no additional cost.
5 Embarcadero Center, San Francisco, CA 94111
PLACEHOLDER — per-city transport notes. Needs a new CMS field on Events.
PLACEHOLDER — on-site parking and rates.
PLACEHOLDER — step-free access and hearing loop detail.
PLACEHOLDER — recommended hotels and negotiated rates.
PLACEHOLDER — entrance, level and registration desk location.
PLACEHOLDER — business casual, to confirm.
End users only. CISOs, Heads of Identity, IAM and PAM, identity architects and engineers. Vendors attend as partners.
Every session, networking breakfast and lunch, closing drinks, and opt-in 1 to 1 meetings with partners.
Free for qualified end users. There is no ticket price and no upsell.
No vendors attend unless they are sponsoring. The audience is real end users, many of whom engage with Clutch year-round through roundtables and briefings, so you are not walking into a cold room.
Built to drive interaction through roundtables, simulations, small group activities and workshops rather than slide after slide.
Ten partners maximum per event, so attendees do not get sponsor fatigue and booth engagement stays high.
Attendees choose who they meet, so every meeting is opted in. We do not charge for extra meetings — some sponsors get 10 to 15 at no additional cost.
Audience profile drawn from the Enterprise AI Strategy and AI Engineering summits: 559 practitioners from 312 organisations.
Prices are per event in USD, ex tax. Discounts stack across regions up to 20%.
| Package | Per event | Onstage | Passes | Investment |
|---|---|---|---|---|
| Keynote | 1 | 30-min solo | 5 | $27,000 |
| How I Solved (Demo) | 3 | 15-min solo | 4 | $18,000 |
| Speaker Dinner | 1 | — | — | $16,500 |
| Panel | 2 | Panel seat | 4 | $15,500 |
| Roundtable | 10 | — | 3 | $13,000 |
| Exhibition | 14 | — | 2 | $7,500 |
| Technical Workshop | 1 | 40-min workshop | — | $5,000 |
| Demo Theatre | 5 | 10-min theatre | — | $3,000 |
Because the room is curated, every application is checked against the audience criteria before it is confirmed.
Yes, for qualified end users. There is no ticket price and no upsell.
Only as partners, capped at ten per event. That cap is what keeps the ratio in the room honest.
The value of the room is who is in it. Reviewing keeps the audience practitioner-only.
PLACEHOLDER.
PLACEHOLDER — confirm whether there is a per-organisation cap.
PLACEHOLDER — link to the call for speakers.